Can recruiters reach every client system without a company laptop?
A cloud browser for recruitment agencies runs the browsing session on remote servers and hands each recruiter a session inside a normal tab, so ATS logins, job boards and LinkedIn seats never live on a personal machine. Each client system gets its own profile with its own fingerprint and residential exit IP, and a profile you share with a paid teammate opens already signed in. Nothing is installed on the recruiter’s device, and no password changes hands.

📌 TL;DR Executive Summary
- Core Takeaway: Recruitment work breaks when nine client systems share one laptop, one fingerprint and one IP. A cloud browser gives each system its own isolated session and shares it without handing over credentials.
- Key Risk/Challenge: Candidate passports, bank details and salary data leaking through personal devices, plus LinkedIn’s 2026 enforcement against cloud-proxy automation vendors rather than individual accounts.
- Recommended Solution: Send.win cloud profiles with built-in residential proxies, share-with-login for paid teammates, and the Team-plan automation API pointed at your own ATS instead of at LinkedIn.
A day on a recruitment desk: where the browser breaks
Recruiters don’t work inside one system. A single morning can touch a client’s ATS, two job boards, LinkedIn Recruiter, a shared inbox and a spreadsheet of candidate rates. Here’s how that plays out across one day, and where the browser stops being a neutral tool.
07:40 — the client ATS sweep
You sign into Bullhorn for one client, a guest seat in another client’s own system, and a job-board inbox for a third. Four systems, four logins, one laptop. All four inherit the same IP address, canvas hash, font list and screen size. Nothing breaks today. It breaks the first time a platform flags one of those sessions and writes that fingerprint into its abuse graph.
Discipline doesn’t fix this. The fix is one-click account switching between isolated profiles, so the client ATS never shares a session with the job board.
10:15 — sourcing, and the session that has to stay clean
LinkedIn is where the risk concentrates. The platform says it detects automation through behavioural analysis, browser fingerprinting and rate-limit monitoring. Mass connection requests, bulk messaging injected into the interface, profile and search scraping, rapid profile viewing and stacked tools sit at the top of its risk list. API-based scheduling, approved CRM integrations and manual activity at normal volume do not.
13:00 — the borrowed laptop problem
Hybrid desks screen candidates from home networks, coworking Wi-Fi and machines you never see. Compromised personal devices and unsecured networks are one reason recruitment agencies are rated as high-value targets. Insider threat is named as a top risk in the sector too, and it covers accident as much as intent — a recruiter dragging a shortlist to their personal drive, or a departing consultant taking a client list.
The same maths applies to the machine you do control. A personal LinkedIn profile and three client systems in one browser install are one fingerprint apart, so keep personal logins in their own profile and out of the work graph.
16:30 — submissions and the handoff
Submissions need speed and evidence. When a login lives inside one Chrome profile on one machine, a sick day stalls the pipeline. Outsourced sourcers make it worse: you either hand a client ATS password to a contractor or you lose the coverage.
The three risks that end agency contracts
1. Candidate PII on machines you don’t control
Recruitment firms hold candidate income, bank details, passport and visa information, client contracts and salary data. That’s the highest-value material in the business and the first thing attackers look for. Only about 10% of enterprises have encrypted 80% or more of their cloud data, while 47% of cloud data is classified as sensitive, according to the Thales Cloud Security 2024 Report. Average breach costs have been put at $4.35 million for 2022 and $4.45 million for 2023 across detection, escalation, notification and response.
2. Account linking: one laptop, nine client systems
When nine accounts run from one browser install, they share a fingerprint and an exit IP. LinkedIn’s User Agreement section 8.2 bans scraping, bots and automated methods of access, plus any attempt to override security features or bypass access limits; the Prohibited Software policy adds third-party tools that automate activity on the service. Enforcement now reaches infrastructure. In March 2026 LinkedIn removed automation vendor HeyReach’s company page and banned its founder over its cloud-proxy browser architecture — a vendor-level takedown, not a user-level warning.
3. Shared logins that outlive the recruiter
Clients and recruitment firms routinely share connected systems, and those shared systems are named attack targets. The operational version of the same problem is credential sprawl: a password pasted into chat, saved in a personal password manager, still working six months after the recruiter left. You can’t audit a login you can’t see.
| Risk | How it shows up on the desk | What removes it |
|---|---|---|
| PII exposure | CVs, passports and salary notes landing in personal download folders | Sessions that run off-device, so the file never reaches the laptop |
| Account linking | Client ATS, LinkedIn and job boards all presenting one fingerprint and one IP | One isolated profile per client system, each with its own fingerprint and residential exit |
| Credential sprawl | Passwords in chat, shared seats, no offboarding trail | Profile sharing that opens already signed in, revoked from one place |
| Insider leak | Departing recruiter exporting pipelines on the way out | Profiles that stay with the agency, not the person |
Cloud browser vs VPN vs VDI for staffing agencies
Teams usually arrive here comparing three options, and they solve different problems. A VPN changes the IP your traffic leaves from, but every account still runs inside one browser on one machine with one fingerprint. A virtual desktop hands you a full remote machine — heavier, provisioned per desktop, and it still doesn’t separate accounts from each other unless you build that in. A cloud browser for recruitment agencies isolates the session itself.
| VPN | VDI | Cloud browser | |
|---|---|---|---|
| What it isolates | Network path only | A whole desktop | Each browser profile and its accounts |
| What the recruiter installs | VPN client | Client or thin terminal | Nothing — it runs in a browser tab |
| Fingerprint separation | None | One desktop image usually means one browser profile | Per-profile fingerprints spoofed at engine level |
| Best fit | One account, one machine | Legacy software that must run on a managed box | Many client systems and job boards per recruiter |
If you want the longer breakdown, there’s a separate piece on cloud browser vs VPN trade-offs for agency teams.
Setting up a cloud browser for recruitment agencies: step by step
The walkthrough below uses Send.win, because that’s the setup this desk pattern is built around. A cloud browser for recruitment agencies runs the profiles on EU and US nodes and needs nothing installed; the Sendwin Browser desktop app covers Windows, macOS and Linux when a recruiter wants local speed. The free preview gives 10 minutes a day of cloud browsing, and Pro and Team lift that cap.
Step 1 — Split profiles by client system, not by recruiter
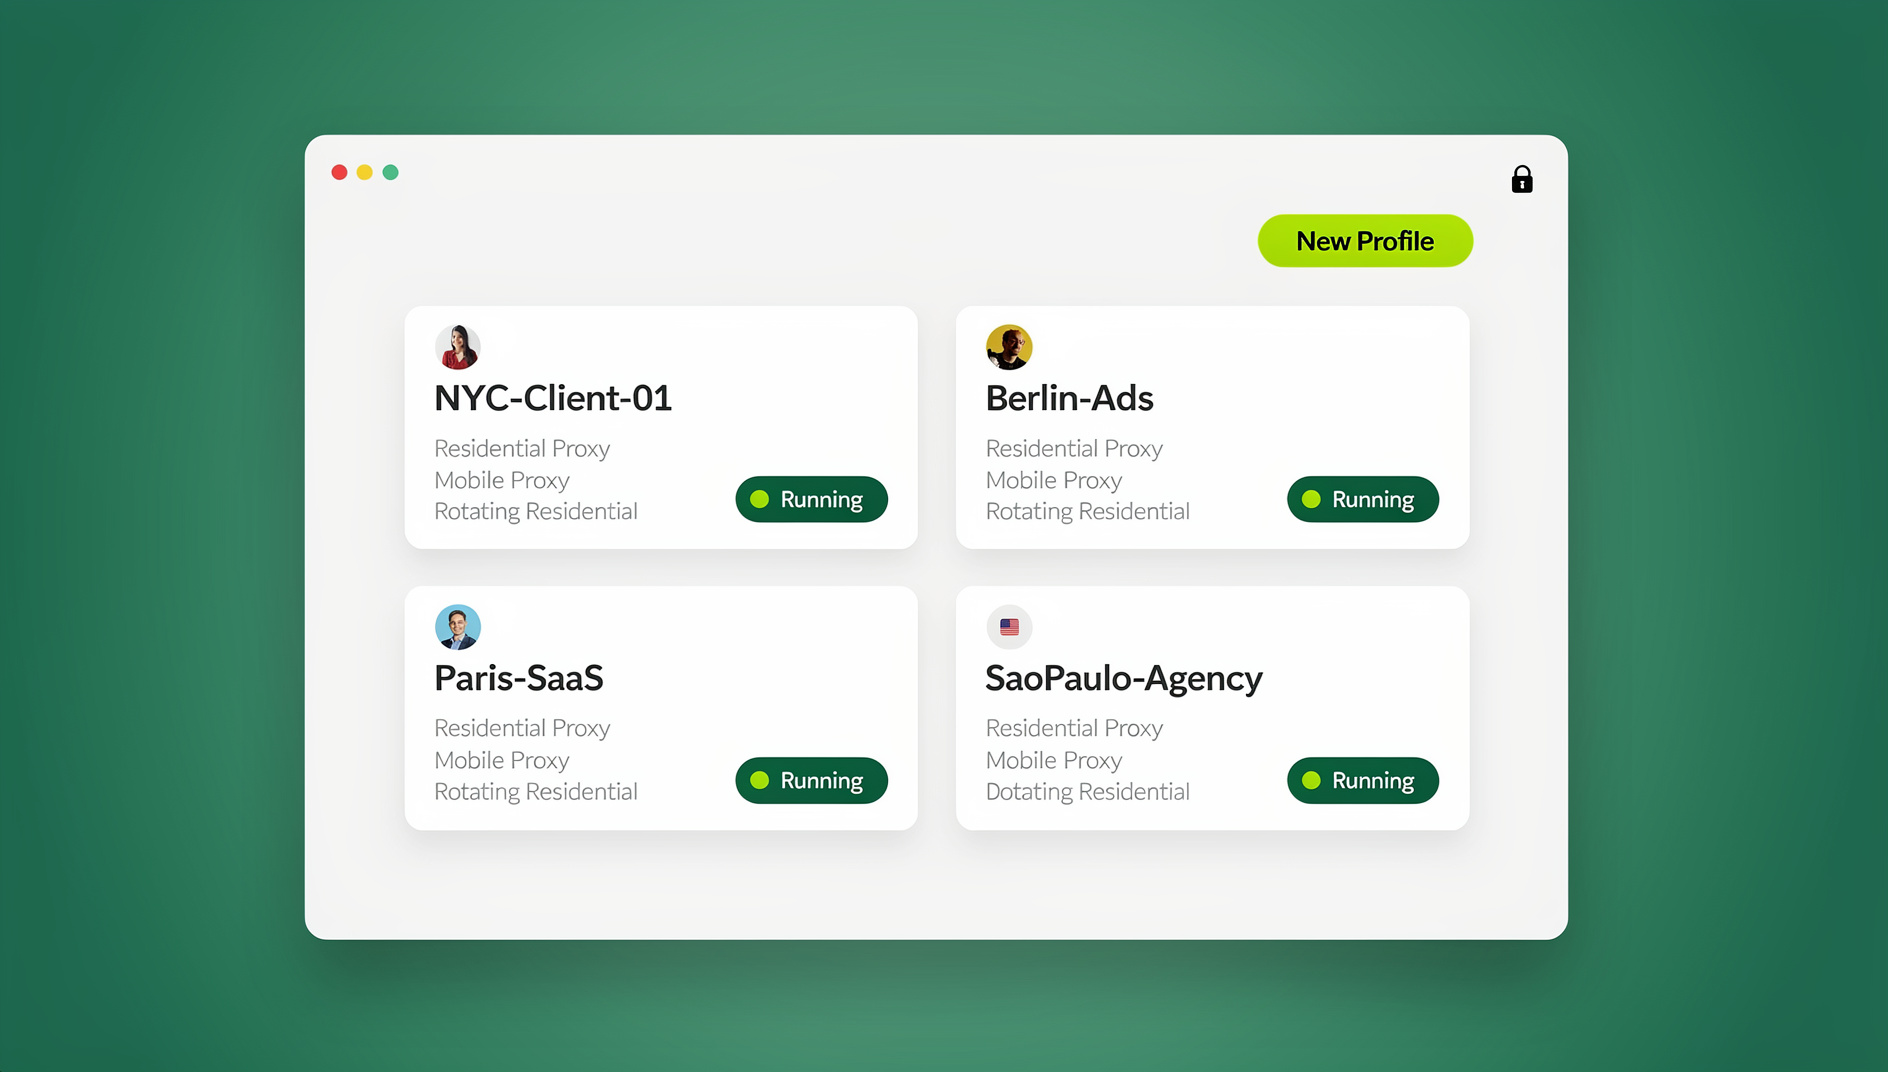
One profile per client system is the rule that prevents linking. A recruiter covering three clients ends up with something like ACME-ATS, ACME-LinkedIn, NORTHCO-JobAdder and one internal CRM profile. Profiles are the unit you name, share and archive — 10 on the free trial, 150 on Pro, 500 on Team.
Step 2 — Attach an exit that matches the client’s market
Every Send.win plan ships built-in residential proxies: 10 on the trial, 20 on Pro and Team, with 1 GB, 5 GB and 20 GB of monthly bandwidth respectively. Residential exits matter because hosting and data-centre ranges are easy to classify, while a consumer ISP address looks like the connection a real applicant or recruiter uses. Timezone, locale, WebRTC and geolocation follow the proxy’s exit IP automatically, so you don’t hand-tune them per profile. If a client insists on a specific region or their own corporate proxy, bring your own HTTP or SOCKS5 instead.
Step 3 — Share the profile so the teammate opens it already signed in
Share a profile with a paid teammate and it opens already logged in. No password leaves your password manager, and nothing needs rotating when a sourcer joins. Pro covers up to 20 paid members, Team up to 50, and live cloud sessions can be shared the same way — which is how someone hands over a half-finished shortlist without screen-sharing their whole desktop. The wider patterns are in this guide to collaboration features for agencies.
Step 4 — Lock the profile down
Block profiles for privacy when a session shouldn’t be touched outside working hours. Cloud sync keeps logins following the recruiter across devices — 20 profiles on Pro, 100 on Team — and encrypted cloud storage holds 1 GB on Pro and 15 GB on Team. Use it for session artifacts, not candidate CVs; the ATS stays the system of record.
Step 5 — Automate the repeat work on your own systems (Team)
Send.win exposes a local Automation API for Selenium, Puppeteer and Playwright on the Team plan only. Point it at systems your agency has a contract with: your ATS, your CRM, your own job-board accounts. Don’t point it at LinkedIn — the user agreement prohibits automated methods of access, and the 2026 enforcement record shows takedowns that reach vendor infrastructure.
The script below attaches to a running Send.win profile and checks the last-contacted date before it writes a submission note, which is the cheapest guard against duplicate outreach.
import csv
from datetime import date, timedelta
from playwright.sync_api import sync_playwright

# Team plan only: local Automation API.
# Copy the CDP endpoint from the profile's automation settings while it is running.
CDP_URL = "http://127.0.0.1:PORT"
ATS_URL = "https://your-agency-ats.example/submissions"
COOLDOWN_DAYS = 21

today = date.today()

with sync_playwright() as p:
    browser = p.chromium.connect_over_cdp(CDP_URL)
    context = browser.contexts[0]
    page = context.pages[0] if context.pages else context.new_page()
    page.goto(ATS_URL)

    with open("shortlist.csv", newline="") as handle:
        for row in csv.DictReader(handle):
            page.fill("#candidate-search", row["email"])
            page.click("#search-button")
            page.wait_for_selector("#last-contacted")

            last = page.inner_text("#last-contacted").strip()
            if last:
                days_since = (today - date.fromisoformat(last)).days
                if days_since < COOLDOWN_DAYS:
                    print("skip, contacted recently:", row["email"])
                    continue

            page.click("#open-candidate")
            page.fill("#submission-note", row["note"])
            page.click("#save-submission")
            print("submitted:", row["email"])
LinkedIn in 2026: what your sourcing team can and cannot do
Keep the platform rules separate from the tooling. A cloud browser for recruitment agencies changes where the session runs; it does not change what the platform permits. LinkedIn’s User Agreement prohibits scraping, bots, automated access, overriding security features and bypassing access limits, and its Prohibited Software policy rules out third-party tools and extensions that automate activity. hiQ Labs v. LinkedIn (2017–2022) established that scraping publicly available data isn’t a federal crime under the Computer Fraud and Abuse Act — but LinkedIn still won that case on breach-of-contract grounds, which is the part that costs agencies their seats.
What actually gets accounts restricted is behaviour and volume, not the browser: bulk connection requests, bulk messaging pushed into the interface, rapid profile viewing, and stacking three tools on one account. The escalation gap has also shortened — accounts that drew a soft warning in 2024 can see feature restrictions within days in 2026. LinkedIn publishes no enforcement statistics, so any precise ban-rate percentage you read online is fabricated. The one large published dataset comes from a verified API vendor, 441,965 outreach sequences with recoverable temporary rate-limiting as the only recorded failure mode, and that describes API architecture rather than browser sessions.
The practical rule: keep LinkedIn in its own profile on a residential exit, let recruiters work manually at human volume, and route anything scheduled through approved integrations. If a client’s LinkedIn Recruiter seat is involved, that seat gets its own profile too.
Scaling from five recruiters to fifty
The setup that works for five people breaks in predictable places at fifty. Scaling a cloud browser for recruitment agencies means planning for four of them.
- Seat handoffs. Remove the teammate from the share list, rotate the underlying account password once, keep the profile and its history. The profile belongs to the agency, not the person.
- Offboarding. Revoke shares the day someone hands in notice, before they export anything. Because logins live in profiles rather than laptops, that’s one action instead of a password-reset project across nine systems.
- Cloud session concurrency. The free preview runs one cloud session, Pro runs three and Team runs nine at once. Sourcing sprints need the Team headroom; steady desk work rarely does.
- Add-ons instead of plan jumps. Extra proxy bandwidth is $6 per GB and extra profiles are $0.05 each, so one busy quarter doesn’t force a plan change.
Run Cloud Browser For Recruitment Agencies in the Cloud With Send.win
Send.win’s cloud browser runs your isolated profiles on remote infrastructure — open a clean, fingerprint-isolated session from any device without installing anything:
- Instant cloud sessions – launch an isolated browser in seconds, no local install
- Isolated profiles – separate fingerprint, cookies, and storage per session
- Cloud sync & profile sharing – pick up the same profiles on the desktop app (Windows, macOS, Linux) or share them with your team
- Built-in residential proxies – with automatic timezone and locale matching
You can try it right now: the Send.win demo browser opens an isolated cloud session directly in this browser tab. The 30-day free trial needs no credit card, and paid plans start at $6.99/month billed annually — see pricing.
Teams running several client systems per recruiter usually standardise the pattern in one document — the same reason there’s a dedicated guide to running a cloud browser for teams across an entire desk.
The cost math beside your ATS bill
Budget in the right order. Your ATS is the biggest line, browser isolation is the smallest, and the small one decides how safely the big one gets used. Bullhorn’s published small-agency tiers are $99 per user per month for Starter and $165 for Core. A five-seat agency lands at $5,940 a year on Starter or $9,900 on Core; a 15-person agency on Core is $29,700 a year before add-ons. Anything that writes into Bullhorn through the marketplace, or needs LinkedIn Recruiter System Connect, pushes you to Core — roughly 67% above the Starter headline. There’s no free trial, only a demo.
Per-user ATS pricing punishes headcount, so watch the shape of the bill. Send.win’s Team plan is billed per account rather than per recruiter and includes 16 team seats (Pro includes 6), at $49 a month or $20.99 a month billed annually, $251.88 a year. Add the 30-day trial at $0 today and the 7-day money-back guarantee, and the browser layer costs a rounding error next to the systems it protects. Vendor figures on the ATS side — 24% more placements per recruiter, 28% more jobs filled, 13+ hours saved per recruiter per week — are Bullhorn’s own, so weigh them accordingly.
🏆 Send.win Verdict
Recruitment agencies need three things a normal browser can’t give them: sessions that don’t live on personal laptops, client systems that don’t inherit each other’s fingerprint, and seat handoffs that don’t involve emailing a password. Send.win covers all three with cloud profiles on EU and US nodes, residential proxies on every plan, and share-with-login for paid teammates. It won’t automate LinkedIn for you — nothing legitimate will — but it keeps your ATS work isolated, revocable and off the device.
Try Send.win free today — 30 days at $0 today, cancel anytime, plus a free 10-minute daily cloud preview if you want to look before you commit.
Frequently Asked Questions
Can recruiters access ATS and job boards without installing software?
With a cloud browser, yes. The session runs on the vendor’s servers and the recruiter reaches it through a web interface, so there is nothing to install on the laptop. Send.win’s cloud browser runs on EU and US nodes and gives you a free 10-minute daily preview, with unlimited cloud browsing time on Pro and Team. If a recruiter wants local speed instead, the Sendwin Browser desktop app is installed on Windows, macOS and Linux.
How do agencies share client logins without giving out passwords?
They share the profile, not the credentials. A shared Send.win profile opens already signed in for the paid teammate you invited, so no password is typed, copied or rotated. Access is revoked by removing the person from the share list, which takes seconds and leaves the login intact.
Is a cloud browser safe for candidate PII and CVs?
Safer than leaving the same material in download folders across personal laptops. The session runs off-device, residential proxies route the traffic, and encrypted cloud storage keeps session artifacts under the agency’s account. The ATS should stay the system of record for CVs — don’t treat a browser profile as a filing cabinet.
Cloud browser vs VDI for staffing agencies — which is cheaper?
A cloud browser is usually lighter, because you’re isolating one session rather than provisioning and patching a full desktop per recruiter. VDI still makes sense when legacy internal software has to run on a managed machine. Price both against the number of client systems per recruiter, not the number of recruiters.
Can I log into LinkedIn from a cloud browser without getting flagged?
Logging in isn’t the risk; automating is. LinkedIn’s terms prohibit bots and automated access, and enforcement in 2026 reached vendor infrastructure — HeyReach’s company page and its founder’s profile were removed in March 2026. Keep LinkedIn in its own profile on a residential exit, work at human volume, and route scheduled activity through approved integrations. Nobody can promise a flag-free outcome.
How do remote recruiters stop data leaving on personal laptops?
Take the data off the laptop instead of policing the device. When CVs, IDs and salary notes are viewed in a session that never stores them locally, a compromised personal machine has nothing to take. Add profile blocking for privacy and revoke shares at offboarding.
Do job boards block access from cloud or data centre IP addresses?
Hosting and data-centre ranges are easy to classify and are often treated as higher risk, which is why residential exits look like ordinary home connections. Send.win includes residential proxies on every plan, and timezone, locale, WebRTC and geolocation follow the exit IP automatically. If a client insists on a specific region or their own corporate proxy, bring your own HTTP or SOCKS5.
What does Bullhorn actually cost a five-person staffing agency?
On published small-agency pricing, $5,940 a year on Starter at $99 per user per month, or $9,900 on Core at $165 per user per month, before add-ons. Core is the tier that unlocks the partner marketplace, custom fields and LinkedIn Recruiter System Connect. There’s no free trial, only a demo.