What a Cloud Browser Actually Changes for a Logistics Team
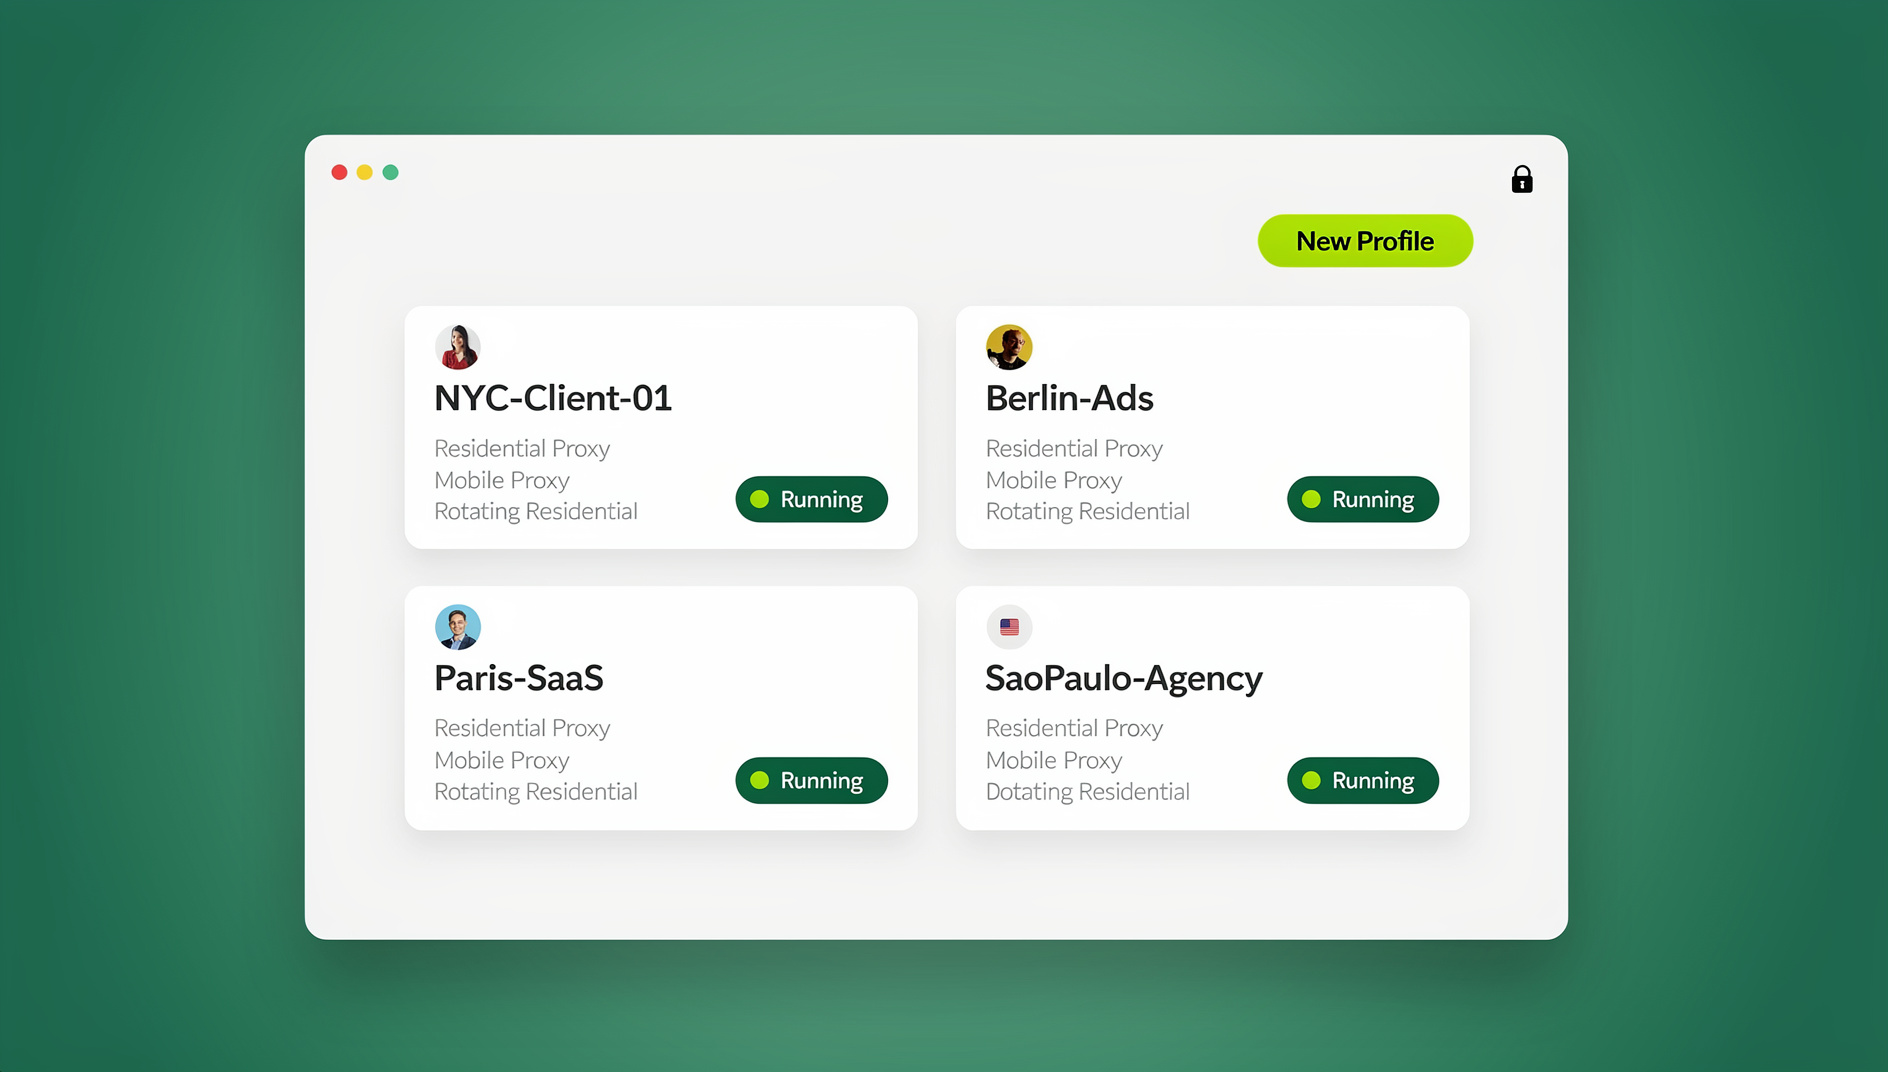
A cloud browser for logistics companies gives each carrier portal, TMS dashboard and customs login its own isolated browser profile, so one dispatcher can work across a dozen systems without those platforms linking every account to one machine. Send.win runs those profiles on EU and US cloud nodes from any device, or locally in its Windows, macOS and Linux desktop app, with built-in residential proxies and a Sendwin Stealth engine that keeps canvas, WebGL, font and hardware signals coherent per profile.
📌 TL;DR Executive Summary
- Core Takeaway: Load boards, TMS dashboards, customs filings and settlement all run behind logins that vendors score for risk. Isolated cloud profiles keep each login on its own fingerprint and its own residential IP, and cloud sync keeps the session with the person instead of the desk.
- Key Risk/Challenge: One shared dispatch password, one office IP and one cookie jar is the exact pattern carrier fraud systems correlate — and the challenge usually lands mid-shipment, when a verification code is on someone else’s phone.
- Recommended Solution: One Send.win profile per entity, region or portal identity, paired with built-in residential proxies and shared with paid teammates instead of passwords, plus the local Automation API on Team for repetitive portal entry.
Logistics is a browser-first job. Load coverage, appointment scheduling, customs filings, rate benchmarking and settlement all happen behind login screens operated by vendors who score every session for risk. A cloud browser isolation layer sits between your team and those screens instead of collapsing all of it into one shared desktop browser.
The volume behind those screens keeps rising: US e-commerce sales reached $340.2 billion in Q2 2026, up 12.2% year over year and 17.1% of total retail sales. TMS adoption has not followed. Roughly 50% of large shippers, 25% of medium-sized shippers and 10% of small shippers run a transportation management system. For everyone else, the system of record is a stack of portal logins — and logins are what gets flagged.
A Day in the Life: Where Logistics Logins Pile Up
Take a mid-size 3PL with 40 trucks, a brokerage desk and a small cross-border forwarding arm. Here is what the browser layer carries on an ordinary Wednesday.
06:30–08:00: Dispatch and load coverage
A dispatcher opens the load board, the TMS and two carrier onboarding portals before the first coffee. Each wants a location, a timezone and an authenticated session. Run all of it in one window on one shared login and every carrier sees the same device fingerprint, the same cookie jar and the same office IP. The correlation starts here, hours before anything gets blocked.
08:00–12:00: Carrier, broker and customer portals
The networks your team touches are large. Descartes’ Global Logistics Network connects more than 30,000 shippers, carriers and logistics providers. C.H. Robinson’s Navisphere reaches over 540,000 customers and carriers, and FreightPOP centralizes quoting, booking, tracking and auditing across 1,500+ carriers. Every one of those relationships usually arrives with its own login and its own security team.
12:00–16:00: Customs, documentation and warehouse systems
Customs filings, dangerous-goods paperwork and warehouse screens carry legal weight. Vendors push their compliance standards down the chain: CartonCloud, which reports ISO 27001 and SOC 2 certification, counts 600+ businesses and 50,000+ users by its own figures, while Mecalux runs Easy WMS in a SaaS model for multi-client warehouses. When a filing is questioned, “someone on the dispatch login” is not an answer an auditor accepts.
16:00–19:00: Rates, settlement and the e-commerce arm
Afternoon is rates and money. Xeneta benchmarks contract rates from community-sourced data across 300+ shippers and carriers, and Project44 tracks shipments across 1,000+ carriers. Many logistics firms also run a fulfillment arm selling on marketplaces, which adds seller and advertising logins to the same window.
| Window | Who is working | Typical systems open | What has to stay isolated |
|---|---|---|---|
| 06:30–08:00 | Dispatch | Load boards, TMS, carrier onboarding | Cookies and IP per carrier entity |
| 08:00–12:00 | Brokerage and account managers | Customer portals, tracking dashboards | Session identity and MFA state |
| 12:00–16:00 | Customs and warehouse ops | Filing portals, WMS, document uploads | Audit trail and timezone alignment |
| 16:00–19:00 | Pricing and settlement | Rate tools, invoicing, seller hubs | Fingerprint and cookie separation |
Why Portals Flag Logistics Sessions: The Actual Mechanisms
Carrier and TMS risk engines do not mainly score passwords. They score the machine, the network and the behaviour behind the login. Knowing which signal is which tells you what to fix and what to leave alone. A cloud browser for logistics companies addresses all three at once: the profile carries the machine signals, the proxy carries the network, and profile sharing replaces the shared login.
The machine behind the login
Every session leaks a fingerprint: canvas and WebGL rendering, GPU renderer strings, installed fonts, screen metrics and audio stack behaviour. A fingerprint that repeats across six carrier accounts tells the vendor those accounts share a device, and when one account is challenged the pattern is already on file for the rest. Anti-detect profiles spoof those signals at the engine level rather than through script injection, and keep them coherent, so each profile reads like a separate real machine.
The network and the clock
IP reputation, ASN and geolocation matter as much as the fingerprint. A datacenter IP in one country with a browser claiming a different timezone is the classic compromised-account pattern, and the portal answers with step-up verification. This is where offshore back-office teams get caught: same login, same portal, but a network path the vendor already associates with fraud. The fix is a residential exit IP per profile with timezone, locale, WebRTC and geolocation following it automatically — not a corporate VPN that puts everyone behind one address.
Credential sharing and the audit trail
Most dispatch desks run on one mailbox and one password, with the MFA code going to whoever created the account. That creates two problems. Operationally, a 6 a.m. verification request stalls a load when the phone is in another timezone. Legally, when a customs filing or an insurance claim is questioned, you cannot say who submitted it. Many portal terms also prohibit credential sharing between people in the first place, which makes the habit a compliance issue rather than just a hygiene one.
| Risk | How it shows up | What actually fixes it |
|---|---|---|
| Account linking | Several carrier accounts challenged after one flags | One isolated profile per portal identity, each with its own proxy |
| Shared credentials | MFA codes sent to one phone; no record of who acted | Profile sharing with paid teammates instead of password sharing |
| Timezone mismatch | Verification loops on overseas or back-office sessions | Timezone and locale inherited from the proxy exit IP |
| Automation noise | Captchas and throttling on data-entry scripts | Human-paced scripts on saved sessions, not fresh logins |
None of this is exotic security work. It is the same session discipline that cloud browser security best practices describe: treat browser sessions like servers, named and owned and reviewed on a schedule.
Step-by-Step: Setting Up Send.win for a Logistics Operation
You do not need a budget line to test this. The 30-day free trial includes 10 profiles, 10 built-in residential proxies and 1 GB of bandwidth, and it continues on Pro after day 30 if you keep it. A cloud browser for logistics companies gets deployed one named identity at a time, so the order of these steps matters more than the speed.
- Choose where the profiles run. Dispatchers on their own laptops can install the Sendwin Browser desktop app for Windows, macOS or Linux. Teams on locked-down machines, thin clients or shared workstations use the cloud browser: profiles run on Send.win’s EU and US nodes from any device, nothing to install. Free cloud browsing is capped at 10 minutes a day; Pro and Team remove that cap.
- Map your identities before you create anything. One identity per legal entity, per region or per portal login group. A brokerage desk covering loads under two MC numbers needs two identities, not two tabs.
- Name the profiles so nobody has to guess. Something like US-MW-broker-01 or EU-customs-desk. That name is what your team sees in the share list and what you will audit in six months.
- Attach a proxy to each profile. Every plan ships with built-in residential proxies — 10 on the trial, 20 on Pro and Team. If a carrier requires a whitelisted static IP, add your own HTTP or SOCKS5 proxy to that one profile. Timezone, locale, WebRTC and geolocation follow the exit IP automatically, so you never configure them by hand.
- Log in once, inside the profile, and finish MFA there. The session then lives with the profile rather than with your laptop, which removes most of the “who has the code” problem.
- Sanity-check the profile before you load it with real work. Open a fingerprint-check page and confirm the timezone, language and hardware details match the proxy region. Two minutes now saves a support ticket later.
- Share the profile, not the password. A profile shared with a paid teammate opens already signed in, so no password changes hands and no MFA code gets texted around at 6 a.m. Pro supports sharing with up to 20 paid members; Team up to 50.
- Turn on cloud sync for profiles that travel. Pro syncs 20 profiles across devices and Team syncs 100, so an account manager can pick up the same session on a laptop at a customer site.
- Write down an owner and a backup for every profile. This is the step that makes offboarding boring instead of dangerous.
Automating Portal Entry Without Tripping Fraud Checks
Appointment confirmations, proof-of-delivery uploads, tracking updates and rate refreshes are the same handful of steps repeated hundreds of times a week. Send.win’s local Automation API drives Selenium, Puppeteer and Playwright against a profile you already have open, saved session and all. It is a Team plan feature. Gartner projects that by 2028 about 15% of everyday supply chain decisions will be made autonomously, and the repetitive portal work you remove now is the groundwork for that.
The endpoint comes from the profile itself. Open its automation settings, copy the local address and paste it into your script. Never guess the port.
from playwright.sync_api import sync_playwright

# Copy this from the profile's automation settings — the port differs per profile.
CDP_URL = "http://127.0.0.1:PORT"
PORTAL_URL = "https://portal.example.com/appointments"  # your carrier or TMS portal

with sync_playwright() as p:
    browser = p.chromium.connect_over_cdp(CDP_URL)
    context = browser.contexts[0]      # the profile's existing, already signed-in session
    page = context.pages[0] if context.pages else context.new_page()

    page.goto(PORTAL_URL, wait_until="domcontentloaded")
    page.wait_for_selector("table#appointments tbody tr")

    rows = page.locator("table#appointments tbody tr")
    for i in range(rows.count()):
        cells = rows.nth(i).locator("td")
        print(cells.nth(0).inner_text(), "|", cells.nth(2).inner_text())

    # Confirm appointments one at a time, with a pause that looks like reading.
    for reference in ["REF-1001", "REF-1002"]:
        page.get_by_label("Reference").fill(reference)
        page.get_by_role("button", name="Confirm").click()
        page.wait_for_timeout(1200)
Three habits keep automated portal work out of trouble. Run scripts against saved profiles instead of logging in fresh each time, because a new login from a new IP at machine speed is the exact pattern that triggers a challenge. Add human-scale pauses between actions. And automate only what the portal permits — if a carrier’s terms restrict automated submission, that rule stands no matter how clean the fingerprint is.
Scaling From One Dispatcher to a Multi-Region Team
Profile counts grow faster than headcount, because every entity, region or portal group adds an identity. Here is what changes as you scale.
| Capability | Free trial | Pro | Team |
|---|---|---|---|
| Saved browser profiles | 10 | 150 | 500 |
| Built-in residential proxies | 10 | 20 | 20 |
| Proxy bandwidth per month | 1 GB | 5 GB | 20 GB |
| Cloud browsing time | 10 min/day | Unlimited | Unlimited |
| Concurrent cloud sessions | 1 | 3 | 9 |
| Cloud profile sync | — | 20 profiles | 100 profiles |
| Share profiles & live cloud sessions | — | Up to 20 paid members | Up to 50 paid members |
| Automation API (local) | — | — | Included |
| Team seats | 1 | 6 | 16 |
Two things usually decide the jump from Pro to Team: the Automation API and sharing volume. If scripts run occasionally, stay on Pro at $19 a month, or $6.99 a month billed annually at $83.88 a year. Once a dispatch desk automates portal entry daily and needs more seats, Team is $49 a month, or $20.99 a month billed annually at $251.88 a year.
Add-ons stop you from overbuying a tier. Extra proxy bandwidth is $6 per GB and extra profiles are $0.05 each on Pro and Team. Every plan already runs unlimited local profiles at once with no concurrency cap, so bandwidth is usually the limit that bites first.
Once more than three people depend on the same profile, treat it like shared infrastructure with a documented owner and a change log. The ownership habits that cloud browser for teams rollouts codify matter more than the tooling, because the tooling only works if someone owns the profile list.
Cloud Browser vs VPN vs VDI: What Actually Fixes the Problem
Most logistics teams start with a VPN because it is the tool they already own. It solves the wrong half of the problem.
| Approach | What it separates | What it leaves exposed |
|---|---|---|
| Office network or VPN | Hides the office IP address | One cookie jar and one fingerprint behind every portal login |
| VDI / remote desktop | Moves the machine off the desk | Everyone in the VDI still shares browser state unless profiles are separated |
| Cloud browser profiles | Fingerprint, cookies, storage and proxy per identity | Nothing by itself — it still depends on one identity per profile |
A VPN hands everyone behind it the same exit IP, which is the opposite of what carrier portals want to see when several entities share an office. A cloud browser for logistics companies gives each profile its own fingerprint and its own residential proxy, and cloud sync moves that session to another device intact. If you are weighing the two, this breakdown of cloud browser vs VPN covers the trade-offs in more detail.
🏆 Send.win Verdict
For a logistics team, the value is not the stealth engine on its own. It is that every carrier portal, TMS and customs login gets a coherent machine of its own, with timezone and locale inherited from the proxy instead of hand-configured. Profile sharing replaces the shared-password habit, cloud sync keeps sessions with the person rather than the desk, and the local Automation API on Team takes the grind out of appointment and POD entry while attaching to sessions that are already signed in. Test it against your real portal mix before you commit a whole desk to it.
Try Send.win free today — 30 days for $0 with 10 profiles and 10 built-in residential proxies, cancel in two clicks.
Frequently Asked Questions
What is a cloud browser for logistics companies?
It is a browser that runs portal sessions in isolated profiles on remote infrastructure or in a local app, instead of inside one shared desktop browser. Each profile keeps its own cookies, storage, fingerprint and proxy, so a carrier portal sees a consistent individual machine. Send.win runs profiles on EU and US cloud nodes from any device, and offers a desktop app for Windows, macOS and Linux when you prefer local execution.
Run Cloud Browser For Logistics Companies in the Cloud With Send.win
Send.win’s cloud browser runs your isolated profiles on remote infrastructure — open a clean, fingerprint-isolated session from any device without installing anything:
- Instant cloud sessions – launch an isolated browser in seconds, no local install
- Isolated profiles – separate fingerprint, cookies, and storage per session
- Cloud sync & profile sharing – pick up the same profiles on the desktop app (Windows, macOS, Linux) or share them with your team
- Built-in residential proxies – with automatic timezone and locale matching
You can try it right now: the Send.win demo browser opens an isolated cloud session directly in this browser tab. The 30-day free trial needs no credit card, and paid plans start at $6.99/month billed annually — see pricing.
Will isolated profiles stop my carrier accounts from being linked?
Isolation removes the technical correlation: separate fingerprints, separate cookie jars, separate residential exit IPs. It does not change the business relationship behind those accounts, and it does not make a shared credential safe. Keep one profile per entity or portal identity and the linking signals stop lining up.
Do I still need a VPN if I use Send.win?
Usually not for portal access. Each profile already routes through a residential proxy, and timezone, locale, WebRTC and geolocation follow that exit IP automatically. Keep a VPN for general corporate traffic if IT policy requires one, but do not stack it in front of a profile’s proxy, because that reintroduces the shared address.
Is using isolated profiles against carrier portal terms?
Read the terms that apply to you. Many portals prohibit credential sharing between people, which is exactly what profile sharing avoids. Automated submission and scraping are separate questions and are often restricted, so check before pointing a script at any portal.
How much does this cost for a dispatch team?
The 30-day trial is free with 10 profiles, 10 residential proxies and 1 GB of bandwidth. Pro is $19 a month, or $6.99 a month billed annually at $83.88 a year, covering 150 profiles, 20 proxies and sharing with up to 20 paid members. Team adds the local Automation API, 16 seats and 20 GB of bandwidth at $49 a month, or $20.99 a month billed annually.
Can I automate TMS and portal data entry?
Yes, on the Team plan, through the local Automation API that works with Selenium, Puppeteer and Playwright. Your script connects to an already-open profile, so the saved login and fingerprint stay in place. Add pauses between actions and automate only what the portal permits.
What happens when a dispatcher leaves the company?
You revoke the profile share. Because nobody handed over passwords, there is no reset, no shared inbox to rebuild and no session sitting on a departed employee’s laptop. The profile stays with the company, and the next person opens it already signed in.
Does my team need to install anything?
Not for the cloud option. Send.win’s cloud browser runs profiles on EU and US nodes and works from any device with a browser; the free preview gives you 10 minutes a day, and Pro and Team remove that cap. Install the desktop app on Windows, macOS or Linux when you want local execution, which is where the automation API attaches.