5 Steps to Integrate Cloud Browser APIs into Your Workflow
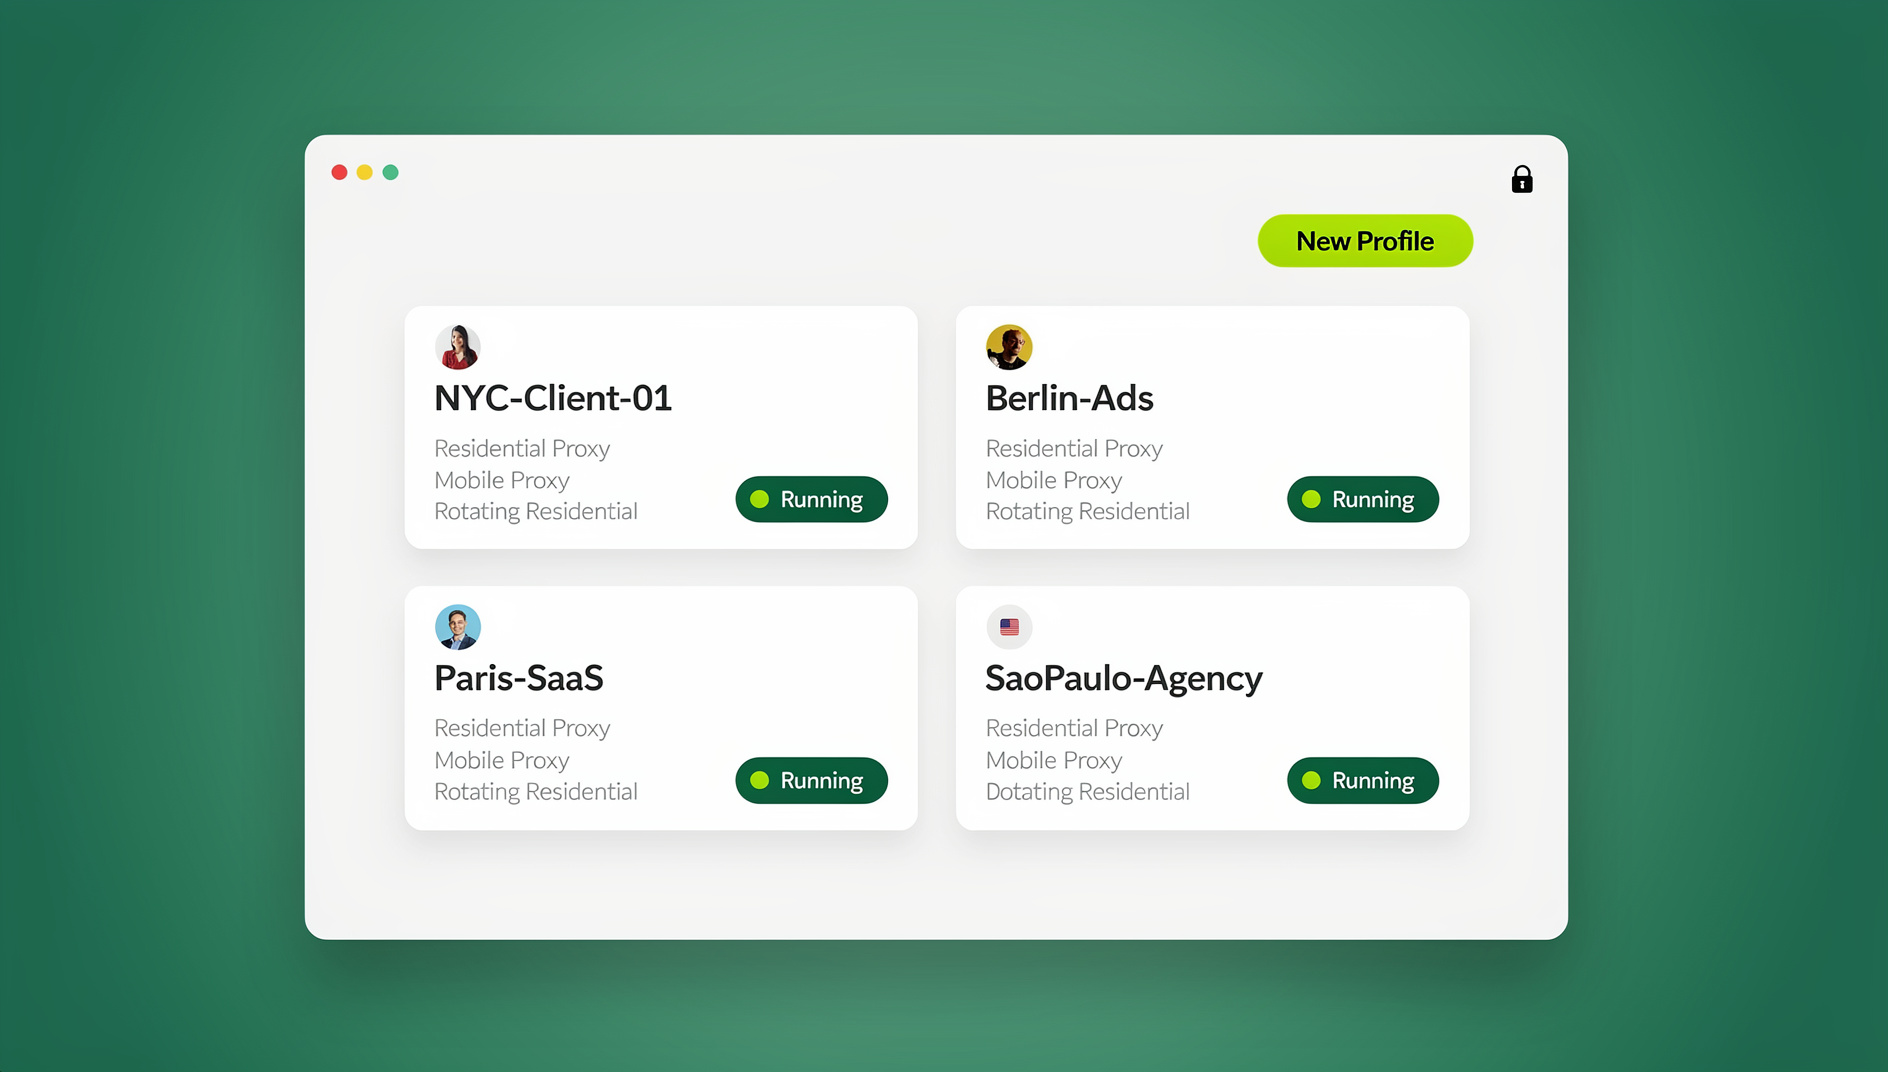
A cloud browser integration guide enables developers to launch, configure, and manage isolated browser environments with their own cookies, storage, sessions, fingerprint settings and proxy. By assigning residential proxies and organising profiles per project, engineering teams can scale multi-account work without managing local infrastructure. Send.win provides isolated browser profiles on both Pro ($19/mo) and Team ($49/mo) plans.
Why Engineering Teams Are Shifting to Programmatic Cloud Browsers
Modern web applications rely on aggressive bot mitigation frameworks, canvas fingerprinting, TLS browser fingerprinting, and IP reputation scoring to detect automated traffic. Traditional headless browsers running on local servers or CI/CD runner environments fail frequently because their HTTP headers, WebGL renderers, user-agent signatures, and IP addresses expose their synthetic nature instantly. Implementing a structured cloud browser workflow allows software developers and data engineers to separate test logic from execution environment management.
When executing scripts against complex websites, maintaining persistent browser profiles with distinct digital identities is paramount. Rather than constructing custom anti-detection layers from scratch, leveraging a specialized cloud browser API handles underlying browser binary customization, hardware spoofing, and proxy routing automatically. This architectural shift significantly reduces test failure rates, prevents account suspensions during multi-account scraping, and simplifies parallel job distribution across cloud nodes.
To avoid security blocks and anti-bot triggers during headless execution, developers must pay close attention to underlying browser characteristics. Understanding how security mechanisms evaluate automation tools is essential; for a deep dive into detection vectors, consult our selenium browser fingerprint analysis.
Architecture Overview of Cloud Browser APIs
Integrating a cloud browser API requires an understanding of how local automation frameworks communicate with remote or containerized browser binaries. Instead of launching a local Chrome or Chromium process via standard subprocess execution, your code communicates with an orchestration server via REST endpoints or WebSocket connections over the Chrome DevTools Protocol (CDP).
| Component | Local Automation (Standard) | Cloud Browser (Send.win) |
|---|---|---|
| Binary Execution | Local CPU / RAM on host machine | Remote cloud environment or isolated desktop engine |
| Fingerprint Spoofing | Manual command-line flags (easily detected) | Native kernel-level OS, WebGL, Audio & Canvas masking |
| Proxy Allocation | Configured per script request | Bound to profile metadata with auto-rotation options |
| Session Persistence | Manual cookie dump/restore to disk | Automatic encrypted cloud state sync across profiles |
| Concurrency Scaling | Limited by host RAM/CPU core counts | Scalable parallel execution across cloud runner nodes |
The control flow follows a four-stage lifecycle: profile creation, environment provisioning, driver connection, and teardown. By maintaining session state on dedicated cloud infrastructure, developers eliminate state contamination while ensuring every test run operates within a clean, isolated environment. Implementing robust session isolation guarantees that cookies, cache files, IndexedDB records, and local storage keys never leak between distinct worker threads or user profiles.
Step 1: Profile Creation and Configuration via REST Endpoints
The first phase in any pipeline is instantiating a browser profile with predefined hardware signatures, operating system characteristics, and network settings. Send.win lets you create profiles with their own fingerprint settings, cookies, storage and proxy.
Below is a complete Node.js example demonstrating how to send an HTTP POST request to create a new browser profile configured with custom canvas parameters, language headers, and screen resolution bounds:
const axios = require('axios');

// Configuration for Send.win Local Automation API (Available on Pro & Team plans)
const API_BASE_URL = 'http://localhost:3000/api/v1';
const API_KEY = process.env.SENDWIN_API_KEY;

async function createCloudProfile(profileName, osTarget = 'windows') {
  try {
    const response = await axios.post(
      `${API_BASE_URL}/profiles/create`,
      {
        name: profileName,
        os: osTarget, // 'windows', 'mac', or 'linux'
        browser: 'chrome',
        canvas_mode: 'noise',
        webgl_mode: 'noise',
        audio_mode: 'noise',
        screen_resolution: '1920x1080',
        language: 'en-US,en;q=0.9',
        timezone: 'America/New_York'
      },
      {
        headers: {
          'Authorization': `Bearer ${API_KEY}`,
          'Content-Type': 'application/json'
        }
      }
    );

    console.log(`[Success] Profile Created! ID: ${response.data.profile_id}`);
    return response.data.profile_id;
  } catch (error) {
    console.error('[Error] Profile creation failed:', error.response?.data || error.message);
    throw error;
  }
}

// Example Execution
createCloudProfile('QA_E2E_Runner_01', 'windows');
When creating profiles via API, selecting appropriate operating system targets ensures that HTTP headers line up perfectly with navigator object parameters. Inconsistent pairings—such as sending a Macintosh user-agent string while executing on a Windows kernel—raise immediate flags during anti-bot evaluations. For an in-depth breakdown of how websites assemble digital signatures, read our comprehensive guide on browser fingerprint explained.
Step 2: Assigning Proxies and Network Gateway Rules
A cloud browser environment requires precise network routing to ensure that geographic locations, timezones, and IP addresses align with assigned profile metadata. Assigning proxies programmatically during profile setup prevents IP leakage before the browser binary initializes.
Send.win supports HTTP, HTTPS, SOCKS4, and SOCKS5 proxy protocols with authentication credentials. When configured via the API, the system automatically adjusts the browser profile’s WebRTC handling rules, preventing local IP addresses from leaking through WebRTC STUN requests.
Here is a Python script illustrating how to attach residential or datacenter proxy configurations to an existing Send.win profile before launching execution:
import requests
import json
import os

API_BASE_URL = "http://localhost:3000/api/v1"
API_KEY = os.getenv("SENDWIN_API_KEY", "your_api_key_here")

def attach_proxy_to_profile(profile_id, proxy_host, proxy_port, username, password, proxy_type="http"):
    headers = {
        "Authorization": f"Bearer {API_KEY}",
        "Content-Type": "application/json"
    }

    payload = {
        "profile_id": profile_id,
        "proxy": {
            "type": proxy_type,
            "host": proxy_host,
            "port": int(proxy_port),
            "username": username,
            "password": password,
            "auto_timezone": True, # Automatically matches browser timezone to proxy IP location
            "webrtc_policy": "disable_non_proxied_udp"
        }
    }

    endpoint = f"{API_BASE_URL}/profiles/update-proxy"
    response = requests.put(endpoint, json=payload, headers=headers)

    if response.status_code == 200:
        print(f"✅ Successfully attached {proxy_type} proxy to profile {profile_id}")
        return response.json()
    else:
        print(f"❌ Failed to attach proxy: {response.text}")
        response.raise_for_status()

# Example invocation matching US East residential node
attach_proxy_to_profile(
    profile_id="prof_98234712",
    proxy_host="us-res.proxyprovider.com",
    proxy_port=8000,
    username="customer_user123",
    password="secure_password_pass",
    proxy_type="http"
)
Enabling automated timezone matching (`auto_timezone: True`) solves a common automation detection trap: IP address location mismatching system clock time. If your proxy resides in London (`Europe/London`) while your JavaScript runtime reports Eastern Standard Time (`America/New_York`), anti-fraud scripts mark the session as suspicious instantly.
Step 3: Cookie Injection and Session State Management
Pre-authenticating accounts by injecting valid HTTP cookies and local storage items is a crucial strategy for bypassing login captchas and automated verification challenges. Rather than completing interactive login forms during every execution cycle, developers can inject serialized session cookies directly into the cloud browser state before connecting execution drivers.
Injecting cookies via REST endpoints ensures that when Puppeteer or Playwright opens the target URL, the web server receives valid session tokens immediately. This technique is key to maintaining long-lived automation tasks while helping to bypass anti-bot security gates without solving CAPTCHAs programmatically.
The following Node.js script demonstrates loading a JSON array of standard Netscape/Chrome format cookies and uploading them into a Send.win cloud profile:
const fs = require('fs');
const axios = require('axios');

const API_BASE_URL = 'http://localhost:3000/api/v1';
const API_KEY = process.env.SENDWIN_API_KEY;

async function injectSessionCookies(profileId, cookieFilePath) {
  try {
    // Read JSON cookie file
    const rawCookies = fs.readFileSync(cookieFilePath, 'utf8');
    const cookies = JSON.parse(rawCookies);

    // Format cookies to match browser standards
    const formattedCookies = cookies.map(c => ({
      name: c.name,
      value: c.value,
      domain: c.domain,
      path: c.path || '/',
      secure: c.secure !== undefined ? c.secure : true,
      httpOnly: c.httpOnly !== undefined ? c.httpOnly : false,
      sameSite: c.sameSite || 'Lax',
      expirationDate: c.expirationDate || (Math.floor(Date.now() / 1000) + 86400 * 30)
    }));

    const response = await axios.post(
      `${API_BASE_URL}/profiles/cookies/inject`,
      {
        profile_id: profileId,
        cookies: formattedCookies
      },
      {
        headers: {
          'Authorization': `Bearer ${API_KEY}`,
          'Content-Type': 'application/json'
        }
      }
    );

    console.log(`[Success] Injected ${formattedCookies.length} cookies into profile ${profileId}`);
    return response.data;
  } catch (error) {
    console.error('[Error] Cookie injection failed:', error.response?.data || error.message);
    throw error;
  }
}

// Example usage
injectSessionCookies('prof_98234712', './session_cookies.json');
Step 4: Connecting Automation Drivers (Playwright, Puppeteer & Selenium)
Once the cloud profile is created, proxies assigned, and cookies injected, the next step is running your work inside that isolated profile. Each Send.win profile keeps its own cookies, storage, sessions and fingerprint settings, so profiles do not share one browser identity.
1. Connecting with Playwright (Node.js)
Each Send.win profile keeps its own consistent browser fingerprint, so profiles do not share one browser identity.
2. Connecting with Puppeteer (Node.js)
3. Connecting with Selenium (Python)
Step 5: Managing Headless vs Headful Execution in Cloud Environments
Choosing between headless and headful execution depends on your operational requirements and detection tolerance. Traditional headless Chromium modes leave distinct traces in JavaScript environment variables, such as `navigator.webdriver = true` and `window.chrome = undefined`.
With Send.win, each profile keeps its own consistent fingerprint settings:
- Virtual Headless Mode (Recommended for CI/CD Pipelines): Executes the full Chrome engine inside a virtual X11 display buffer (xvfb). Websites detect a complete GPU rendering stack and standard window frames, even though no physical screen is attached to the cloud server.
- Interactive Headful Cloud Mode: Displays the browser interface inside Send.win’s web application or desktop client, enabling human operators to monitor execution live, step in to solve interactive challenges, or complete manual account checks.
Integrate Cloud Browser Profiles Into Your Workflow With Send.win
Send.win pairs isolated, fingerprint-managed browser profiles with a cloud browser that runs on Send.win’s servers in the EU, so your work stays in profiles that keep their own separate cookies, storage and fingerprint:
- Isolated profiles – each with its own fingerprint, cookies, and storage
- Built-in residential proxies – with automatic timezone, locale, and WebRTC matching
- Desktop app for Windows, macOS & Linux – plus cloud sessions when you don’t want a local install
Try the instant cloud browser demo — no install, straight from your browser. Then compare plans: paid plans from $19/month, and the first card purchase is covered by a 7-day money-back guarantee.
// Example payload setting execution mode via API
const executionConfig = {
  profile_id: "prof_98234712",
  mode: "virtual_headless", // Options: "virtual_headless", "headful", "cloud_stream"
  viewport: {
    width: 1920,
    height: 1080,
    device_scale_factor: 1
  }
};
Advanced Patterns: Scaling Parallel Execution and Robust Error Handling
When running hundreds of concurrent browser sessions across multi-threaded worker nodes, application state management requires resilient retry mechanisms, rate-limiting handlers, and resource cleanup routines.
1. Connection Pooling & Concurrent Queue Processing
To avoid overwhelming cloud resources or exceeding API rate limits, implement concurrency throttling using worker pools or queue libraries such as `p-limit` in Node.js or `concurrent.futures` in Python:
const pLimit = require('p-limit');
const limit = pLimit(5); // Restrict to max 5 concurrent cloud sessions

const profileIds = ['prof_1', 'prof_2', 'prof_3', 'prof_4', 'prof_5', 'prof_6', 'prof_7'];

const tasks = profileIds.map(id => {
  return limit(() => runPlaywrightCloudAutomation(id));
});

Promise.all(tasks).then(() => {
  console.log('All parallel cloud browser automation tasks completed!');
});
2. Exception Cleanup and Resource Reclamation Pattern
Always enclose browser automation logic inside `try…finally` blocks to guarantee that cloud browser profiles are stopped and released even if an unhandled DOM exception occurs:
async function safeAutomationWrapper(profileId, taskFn) {
  let browser = null;
  try {
    const { cdp_url } = await startProfileApi(profileId);
    browser = await chromium.connectOverCDP(cdp_url);
    await taskFn(browser);
  } catch (err) {
    console.error(`[Task Failure] Profile ${profileId}:`, err);
  } finally {
    if (browser) {
      await browser.close().catch(() => {});
    }
    // Always terminate profile to free plan bandwidth and RAM resources
    await stopProfileApi(profileId).catch(() => {});
    console.log(`[Cleanup Complete] Profile ${profileId} safely stopped.`);
  }
}
Comparison: Cloud Browser API vs Local Headless Drivers
Selecting the right browser automation setup impacts operational scalability, maintenance costs, and script success rates. The table below compares building a custom local headless setup against using Send.win’s managed cloud browser:
| Feature & Capability | Custom Local Headless Setup | Send.win Cloud Browser |
|---|---|---|
| Anti-Bot Bypass Rate | Low (frequent Cloudflare / Akamai blocks) | High (Kernel-level canvas, WebGL & audio masking) |
| Setup & Maintenance | High (manual driver updates, xvfb configuration) | Zero maintenance (ready REST & CDP endpoints) |
| Proxy & Timezone Sync | Manual scripting per request | Per-profile proxy and timezone settings |
| Automation API Access | Requires custom proxy wrappers | No |
| Team Sharing & Multi-seat | Complex custom database architecture | Native multi-user profile sharing & seat management |
Troubleshooting Common Integration Issues
Even well-crafted integration pipelines encounter operational hiccups. Below are solutions to common cloud browser API integration errors:
1. `ERR_CONNECTION_REFUSED` on CDP Socket Connection
Symptom: Playwright or Puppeteer fails to connect to the provided WebSocket URL.
Fix: Ensure that the profile has fully initialized before attempting driver attachment. Add a retry loop with exponential backoff when calling `startProfileApi()`, verifying that the HTTP response code is `200 OK` and `cdp_websocket_url` is non-empty.
2. Unexpected WebGL / Canvas Fingerprint Mismatch
Symptom: Bot detection tests highlight WebGL vendor mismatching user-agent claims.
Fix: Verify that `canvas_mode` and `webgl_mode` in your profile creation request are set to `noise` or `block`, rather than `off`. Avoid overriding the user-agent header manually, as doing so bypasses Send.win’s native fingerprint settings.
3. Account Logouts Between Automated Executions
Symptom: Session cookies disappear when re-launching a profile for a new test run.
Fix: Confirm that your teardown routine invokes the `/api/v1/profiles/stop` endpoint cleanly. Abruptly terminating script processes without calling the stop endpoint can cause unwritten cookie jars or local storage buffers to drop from memory before saving to cloud storage.
🏆 Send.win Verdict
Integrating cloud browser profiles doesn’t have to mean struggling with unstable headless Chrome binaries. Send.win provides isolated browser profiles across native desktop and cloud browser environments. With per-profile fingerprint settings, built-in proxy timezone matching, and full profile controls included on Pro ($19/mo) and Team ($49/mo) plans, developers can deploy robust workflows in minutes.
Try the Send.win cloud demo — Preview it in 3 minutes without signup, or get 10 minutes a day with a free account.
Frequently Asked Questions
What is a cloud browser API?
A cloud browser API is a programmatic service that allows developers to launch, control, configure, and monitor browser instances running in isolated environments via REST HTTP endpoints and Chrome DevTools Protocol (CDP) WebSocket connections using frameworks like Playwright, Puppeteer, or Selenium.
Does Send.win offer an Automation API?
Send.win does not offer an Automation API. The Automation API was retired, and there is no API, SDK, headless mode or Selenium/Puppeteer/Playwright support on any plan. Send.win is available on the Pro plan ($19/mo, or $83.88/yr) and the Team plan ($49/mo, or $251.88/yr).
Can I connect Playwright, Puppeteer, and Selenium to the same API?
No. Send.win does not expose Chrome DevTools Protocol (CDP) WebSocket endpoints or remote debugging ports, and there is no Selenium, Puppeteer or Playwright support on any plan.
How does Send.win handle headless browser detection?
Send.win gives each profile its own consistent browser fingerprint, so profiles do not share one browser identity, and each profile keeps its own cookies, storage and sessions.
Do I need to install local software to run cloud browser sessions?
No. While Send.win offers a native desktop client (Sendwin Browser) for Windows, macOS, and Linux, it also supports cloud browser sessions that run entirely in cloud environments without requiring any local software installation.
How are proxies managed when integrating via API?
Proxies can be attached programmatically to any profile via HTTP REST requests. Send.win supports HTTP, HTTPS, SOCKS4, and SOCKS5 proxies and includes automatic timezone matching, WebRTC leak protection, and geographic IP synchronization.
Can multiple team members access automated profiles simultaneously?
Yes. Send.win’s Team plan supports up to 16 seats and 500 profiles with encrypted cloud sync, allowing team members to access, inspect, and manage shared profiles securely.
Is a credit card required to try Send.win?
No. The only free option is the cloud demo at https://send.win/demo-browser/ — a 3-minute preview without signup, or 10 minutes a day with a free account. Paid plans start at $19/mo, and the first card purchase is covered by a 7-day money-back guarantee.